Researchers disabled abandoned Popcorn Time apps to stop botnet attacks
Eye Security researchers found vulnerable Popcorn Time software running globally and registered domains to disable the updater on millions of devices.
Vulnerable software still active worldwide
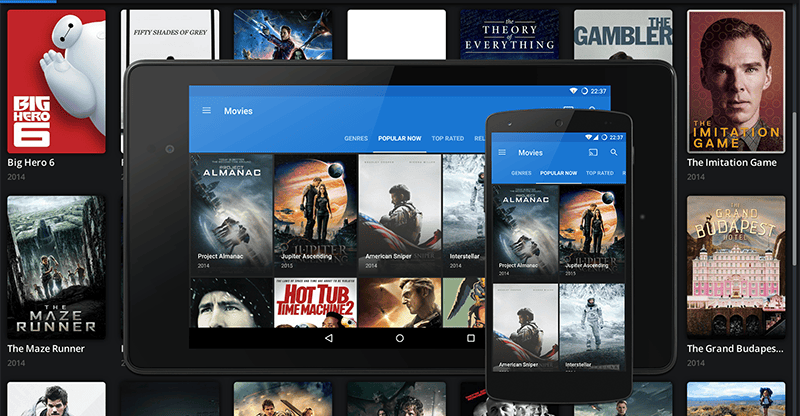
Researchers at Eye Security discovered that an updater for a Popcorn Time fork called Time4Popcorn was still running on Windows, macOS, and Android devices. This outdated software contacted now-abandoned web domains using unencrypted HTTP connections while running an insecure version of Chrome.
Security risks posed by old code
Niels Teusink from Eye Security stated that the updater could allow attackers to install any software with full privileges on a user's computer. The team noted that taking over one of the abandoned domains would enable someone to create a botnet or perform surveillance.
Domain registration stopped the threat
The researchers registered one of the old domains and sent an update instructing the updater to disable itself. They explained that this action was their only alternative because the original update process was not performing any functional tasks.
Reported by one outlet
Only one outlet has published this. Nothing here has been checked against a second report, so read it as that outlet's account and follow the link below for the original.
Reported by
1 independent outlet. Headline as published. Links open the original report.